Vulnerability prioritisation with KEV, EPSS, SSVC and VEX
What to work on, not sorted by severity alone.
In the adminVulnerabilities
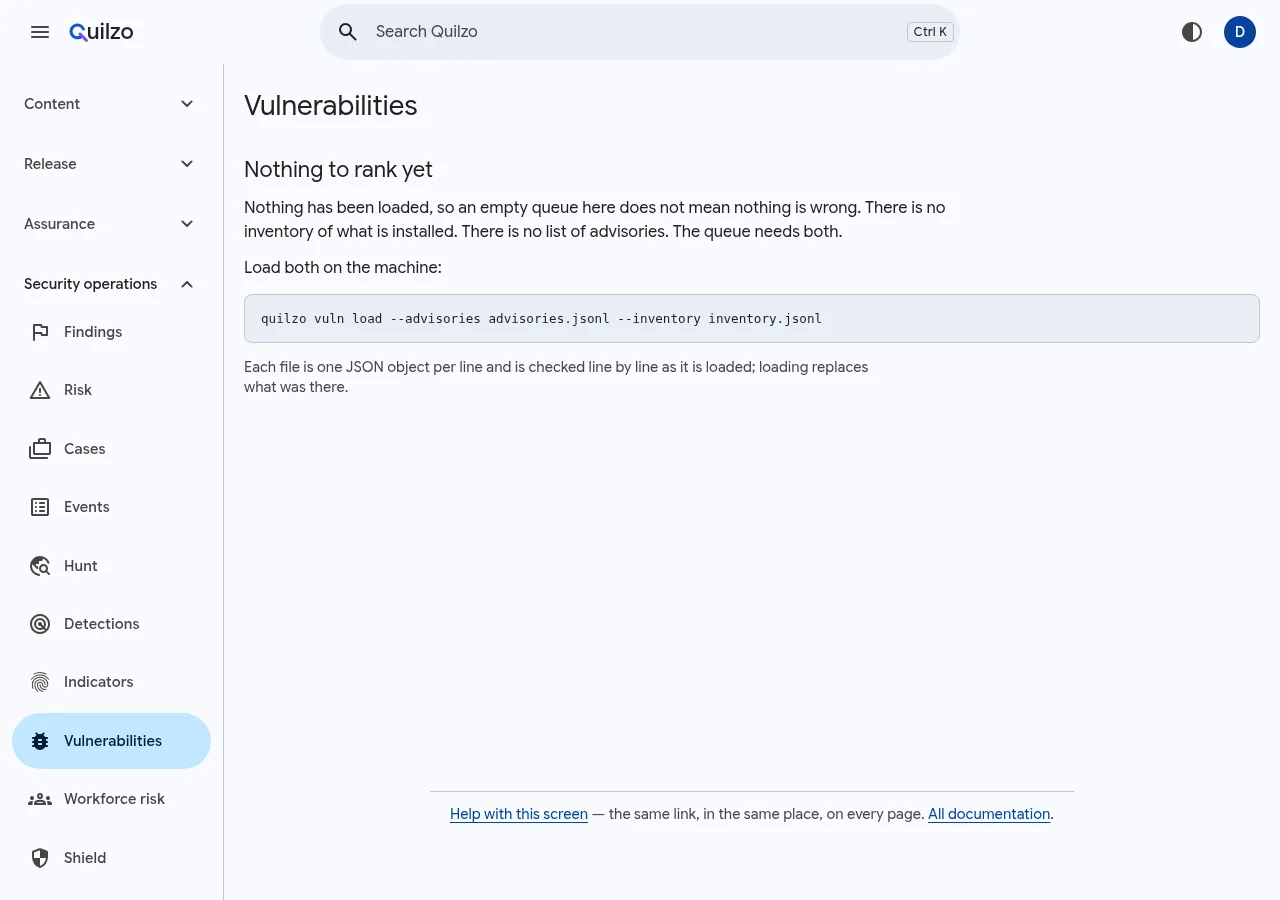
Load what you run and what is known
quilzo vuln import --bom sbom.json --where shop-api --osv osv/ --kev kev.json --epss epss.csvSay what you know about your machines
quilzo vuln asset shop-api --exposure open --impact high --because "..."
quilzo vuln reach --source ./src --where shop-api
Work the queue
To Run What to work on quilzo vuln queueThe smallest upgrades that clear the most quilzo vuln planLeave one, until a date quilzo vuln accept CVE PKG --owner W --until DATE --because "..."Record that it does not apply, and why quilzo vuln assess CVE-ID Go:example.com/lib not_affected --reason vulnerable_code_not_in_execute_path --because "..."Publish your decisions as OpenVEX quilzo vuln vex --author A --id URL