Tamper-evident audit log with signed heads and proofs
Every action recorded, chained, signed and provable entry by entry.
In the adminLog
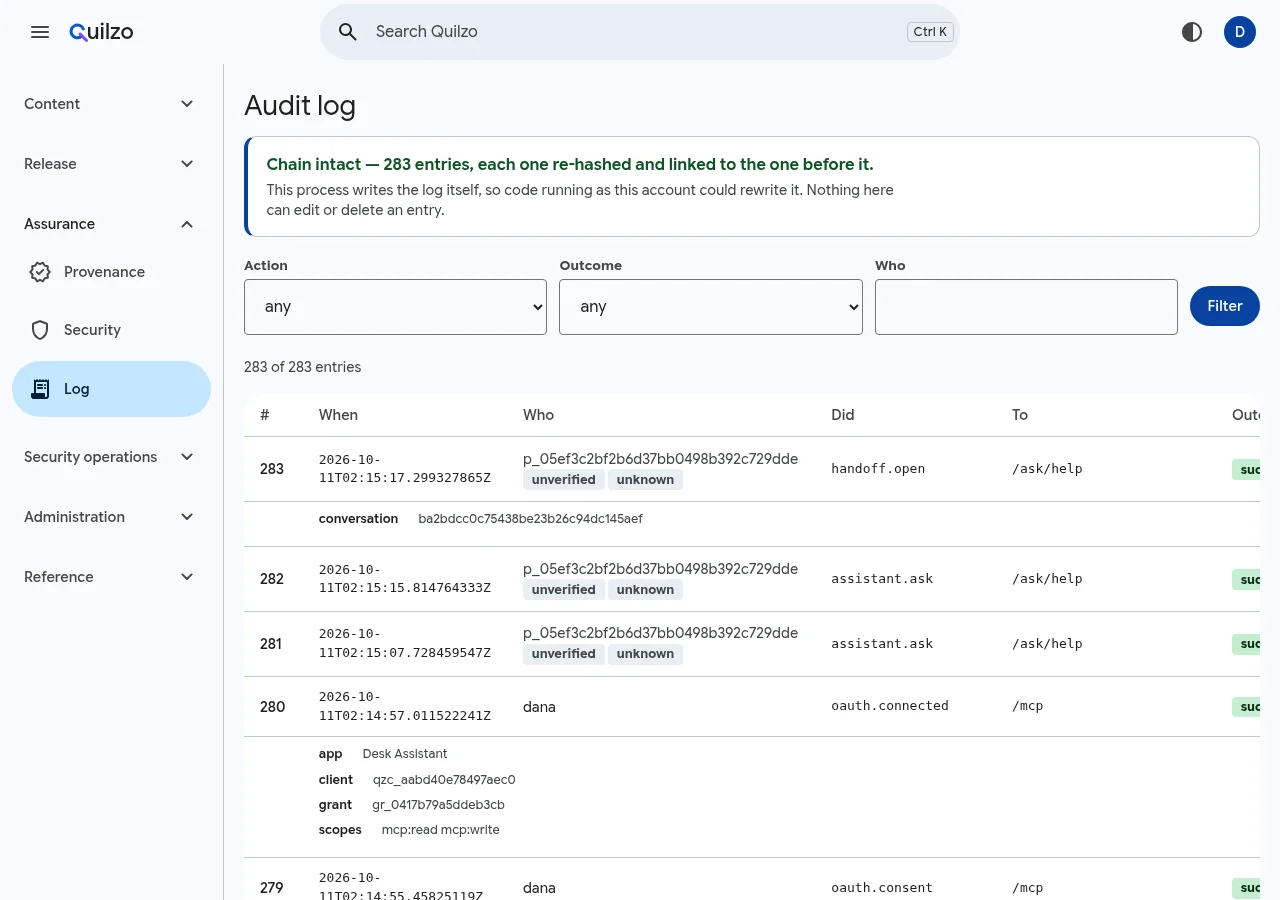
| To | Run |
|---|---|
| Recompute the chain | quilzo auditlog verify |
| One entry in full | quilzo auditlog show SEQ |
| Commit to every entry so far | quilzo auditlog head --save |
| Check a saved head | quilzo auditlog verify-head head.json |
| Prove one entry is in the log | quilzo auditlog prove SEQ |
| Prove nothing before a head moved | quilzo auditlog consistency |
| Anchor the head where you cannot alter it | quilzo auditlog anchor |
| RFC 3161 proof of when you published | quilzo timestamp stamp |
| Run the writer as its own account | quilzo logd |
Identifiers are pseudonymised in the log, and a secret that was refused is never written. Receipts for runs, apps and forgotten memory are built from it (see receipts), and it exports to a SIEM (see traces and the audit log).