The shield: Quilzo defends itself
Decided beforehand, acting at once, and every protection ends by itself.
In the adminShield
The shield is Quilzo protecting itself: playbooks that watch signals such as failed sign-ins, prompt injection against a chatbot or an agent following a planted instruction, and respond at once with protections that always end.
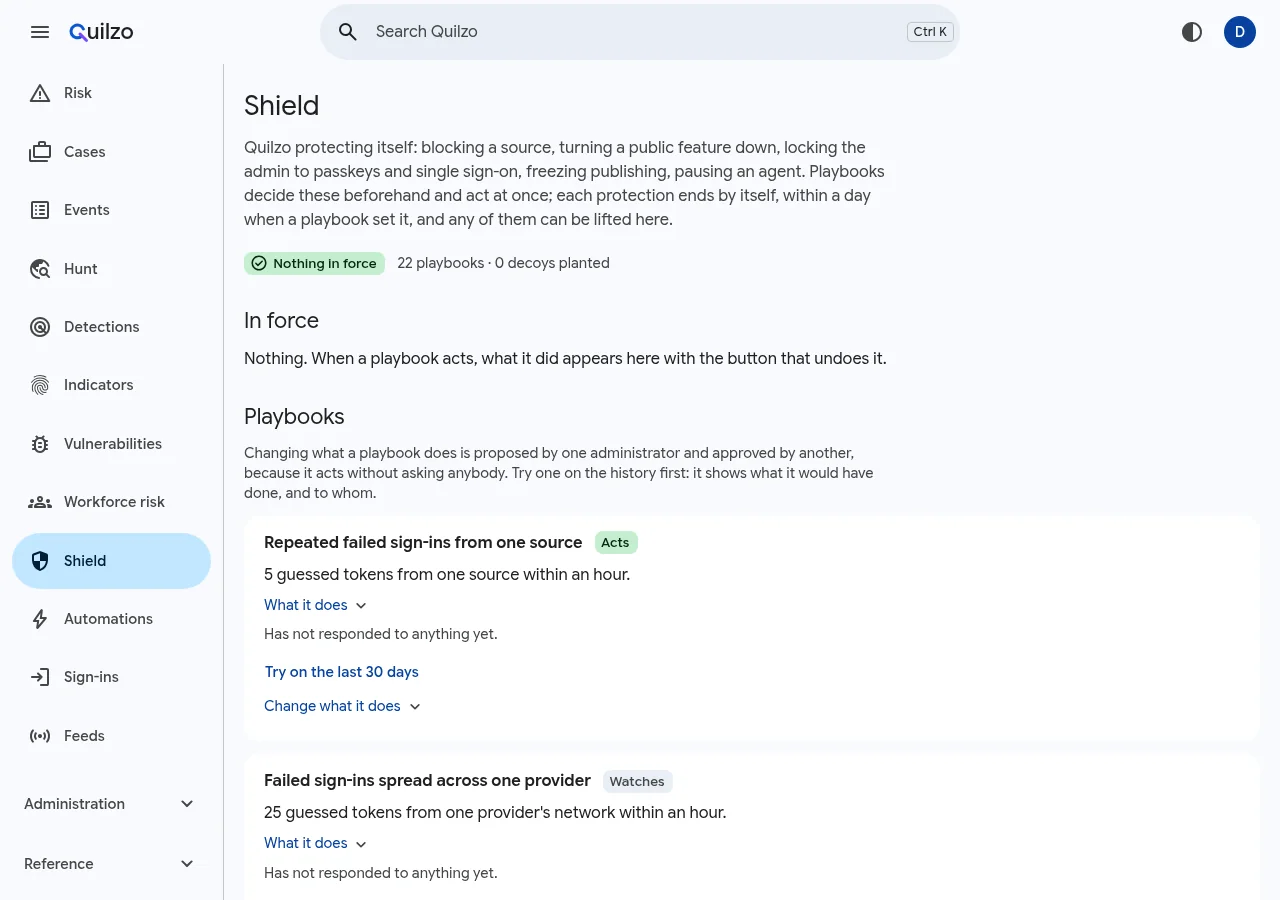
| To | Run |
|---|---|
| What is in force | quilzo shield status |
| End one now | quilzo shield lift ID |
| Block or slow a source | quilzo shield block CIDR --where site --for 1h --reason "..." |
| Turn a public feature down | quilzo shield feature chatbot:help --for 1h --reason "..." |
| Admin to passkeys and SSO only; no publishing | quilzo shield lockdown --for 6h --reason "..." |
| Pause an agent | quilzo shield pause AGENT --for 24h --reason "..." |
| Cut a model route, suspend a credential or app | quilzo shield cut ROUTE / quilzo shield suspend gr_ID |
| See what playbooks would have done | quilzo shield dry-run --days 30 |
| Change a playbook (a second admin approves) | quilzo shield playbook mode NAME act --why "..." |
| Plant a decoy token | quilzo shield decoy add --where "CI variable" |
| Check this build for known flaws | quilzo self check |
It is never turned on the inside: an administrator's own address keeps the admin, internal networks are never blocked, a lockdown nobody could get past is not applied, and the command line on the machine always works.