Passkeys, tokens and sessions
Passkeys for people, scoped tokens for programs, and sessions that end.
In the adminPasskeys
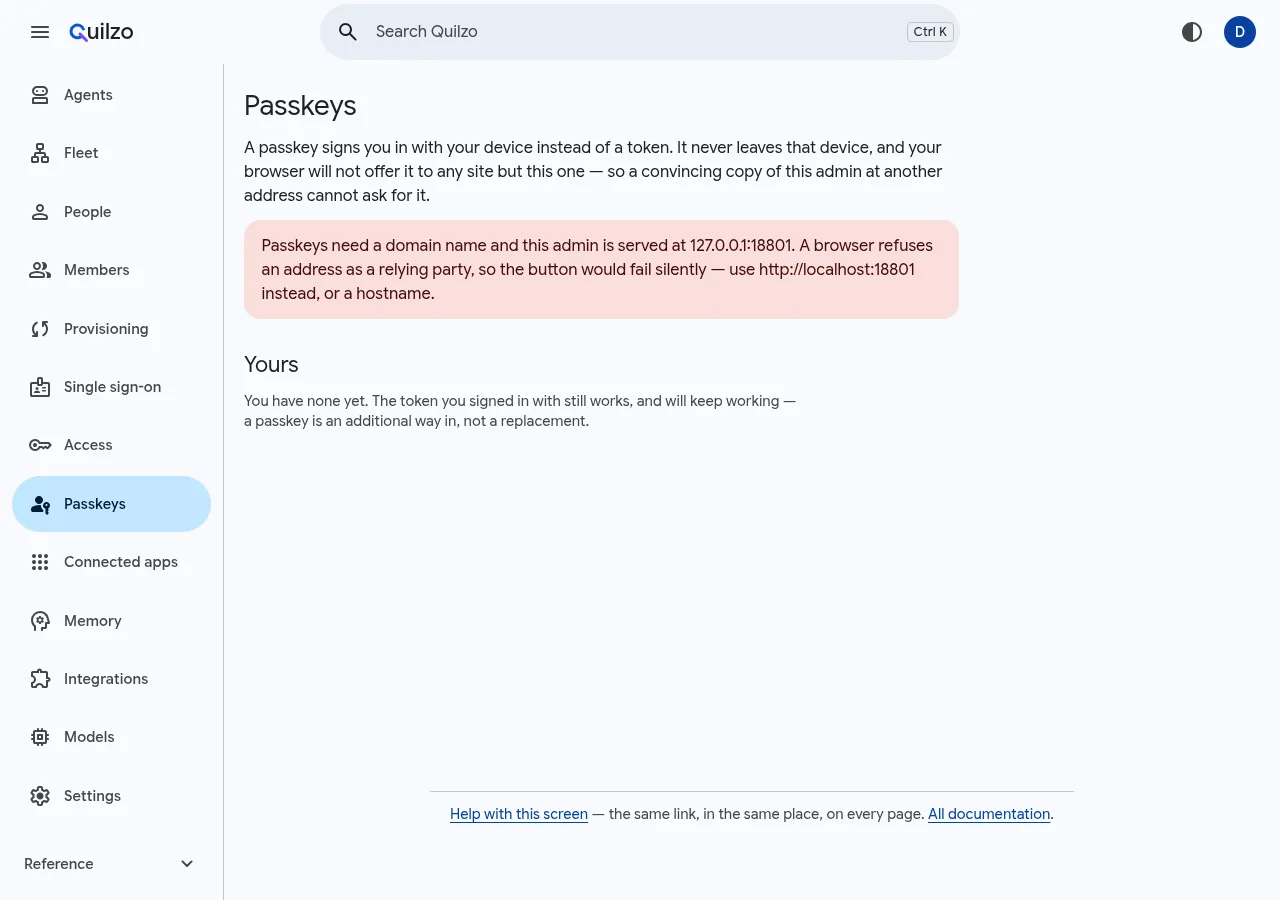
Everybody manages their own passkeys under Administration › Passkeys. There is no password: no password storage, no reset flow and nothing to stuff.
| To | Run |
|---|---|
| Issue a token, a week by default | quilzo token issue nightly --principal deploy --role publisher |
| Let a CI job work with no stored token | quilzo trust add NAME --github OWNER/REPO --as deploy --role publisher (see program credentials) |
| Bind a token to a program's key | quilzo token issue ... --key program.key.pub |
| Short-lived and read-only, for an integration | quilzo token issue ... --api |
| Trade a stored token for a short session | quilzo token exchange |
| List, revoke, find stale ones | quilzo token list / quilzo token revoke ID / quilzo token stale |
A token can carry less than the person holding it, never more. Session limits are organisation policy (see NIST parameters).