Collect security logs from Okta, Entra, GitHub, AWS and more
Get events in: connectors that read, feeds that push, and files that arrive.
In the adminFeedsEvents
Install a connector
Connectors read Okta, Microsoft Entra, GitHub and EVM chains, plus the device and training tools workforce risk uses. Each is a readable manifest that says exactly what it may touch.
quilzo connect catalogue
quilzo connect add okta --org example
quilzo connect secret okta        # from the environment
quilzo connect check okta
Collect on a schedule
quilzo collect run
quilzo collect auto 15m
quilzo collect status
Mappings exist for 17 platforms, including AWS CloudTrail, Google Workspace, Google Cloud, Azure, Kubernetes, CrowdStrike, Cloudflare, Slack, Salesforce and Snowflake. A log that arrives as a file goes in with
quilzo collect file ISSUER/STREAM FILE; your own application's log withquilzo source add MAPPING.json --sample RECORDS.json.Take pushed events
quilzo inbound add okta okta-hooks
quilzo inbound add ssf entra-signals
quilzo inbound add webhook ci-events
Okta event hooks, OpenID Shared Signals (SSF, CAEP and RISC) and signed webhooks.
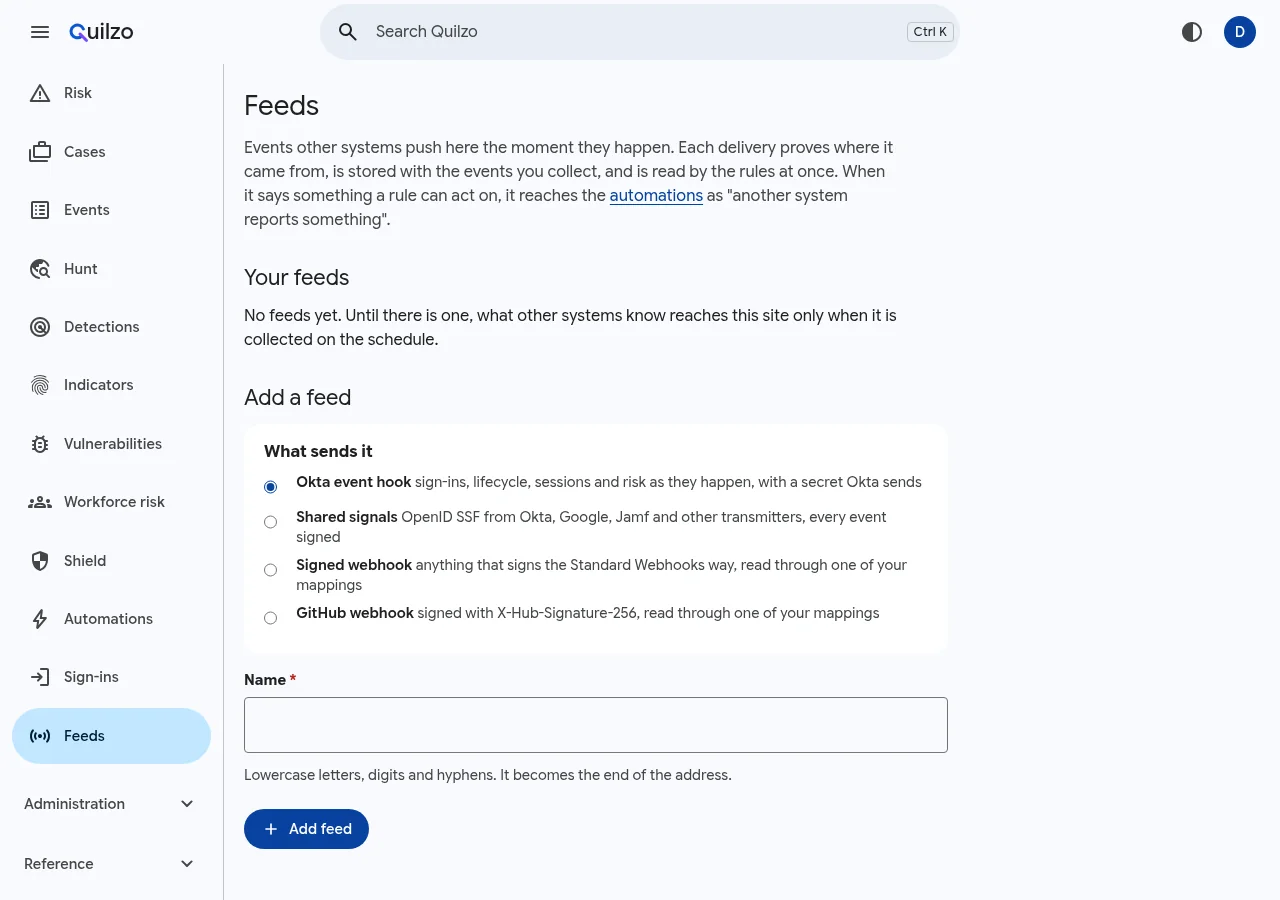
Adding a feed: Okta event hooks, Shared Signals, signed webhooks or GitHub.
Events are stored sealed and digested; quilzo spool verify checks every segment, and quilzo spool hold NAME --why W keeps everything while something is investigated.